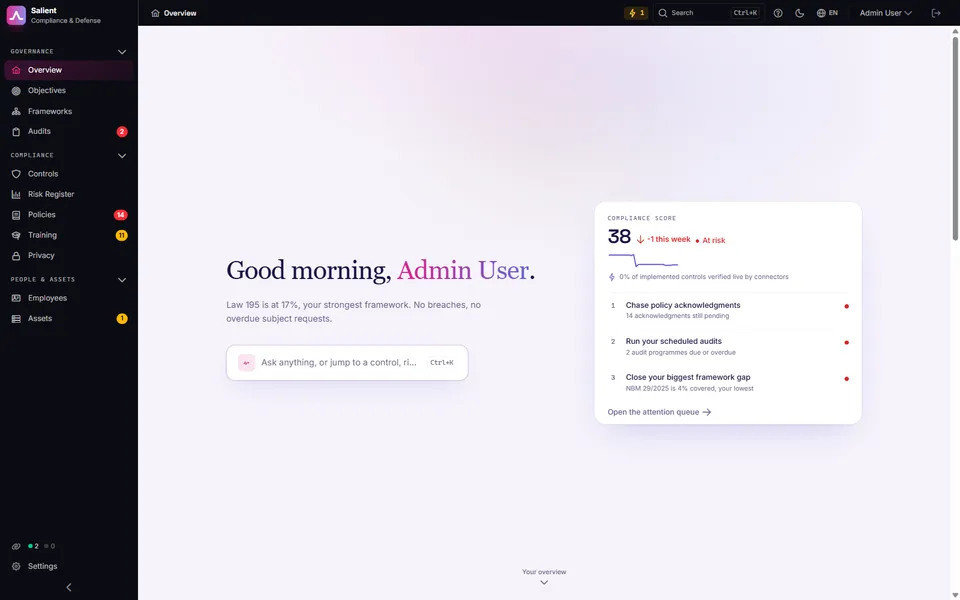
We take over your security function.
ISO 27001, SOC 2, NIS2 and GDPR all expect someone accountable for security, and often a data-protection officer. That function does not require a department. As your external CISO, we keep the policies, the risk register, the vendors, the audits and the relationship with auditors and regulators.