Salient.sec

A compliance platform for ISO 27001, SOC 2, NIS2 and GDPR.

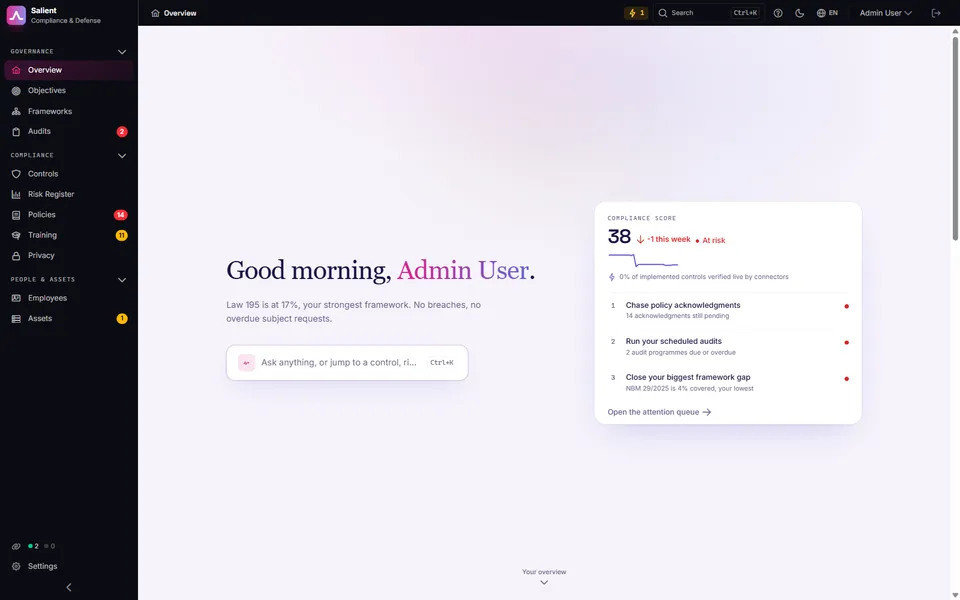
Most companies keep compliance in folders and spreadsheets that get rebuilt before every audit. Salient.sec keeps the list of requirements, who owns each one, what evidence exists and what is missing - current. Built on the international standards, with local regimes mapped on top; English, Romanian and Russian interface.

The Salient.sec overview screen: compliance score and attention queue

01 · Frameworks

Four frameworks, one list of controls.

ISO 27001, SOC 2, NIS2 and GDPR - and local regimes such as Moldova's Law 195/2024, HG 562/2025 and NBM Regulation 29/2025 - are laid over each other. What one framework already covers is ticked for the others, with coverage in plain sight.
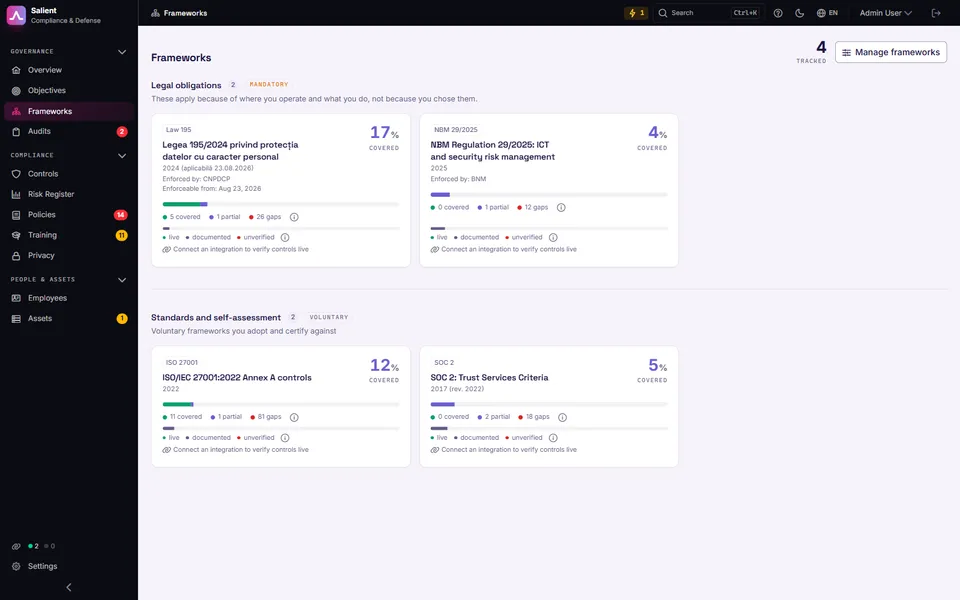
The Frameworks screen: legal obligations and voluntary standards, each with its coverage

02 · Controls

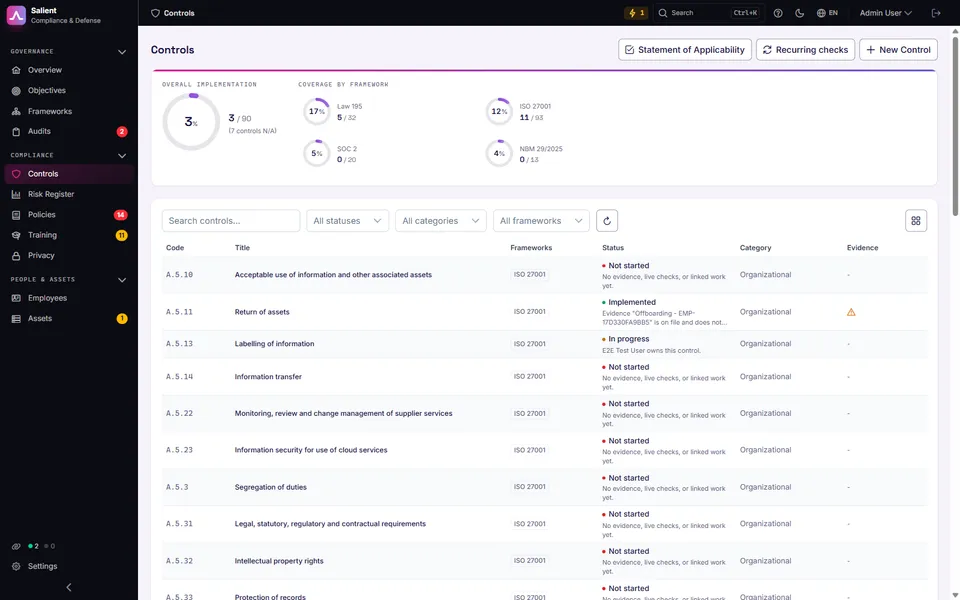
Every control, with an owner, a deadline and evidence.

Statement of Applicability, recurring checks and the real state of each control - implemented, in progress, not started - filtered by framework and category.

The Controls screen: the control list with status, framework and evidence

03 · Data protection

The data-protection module.

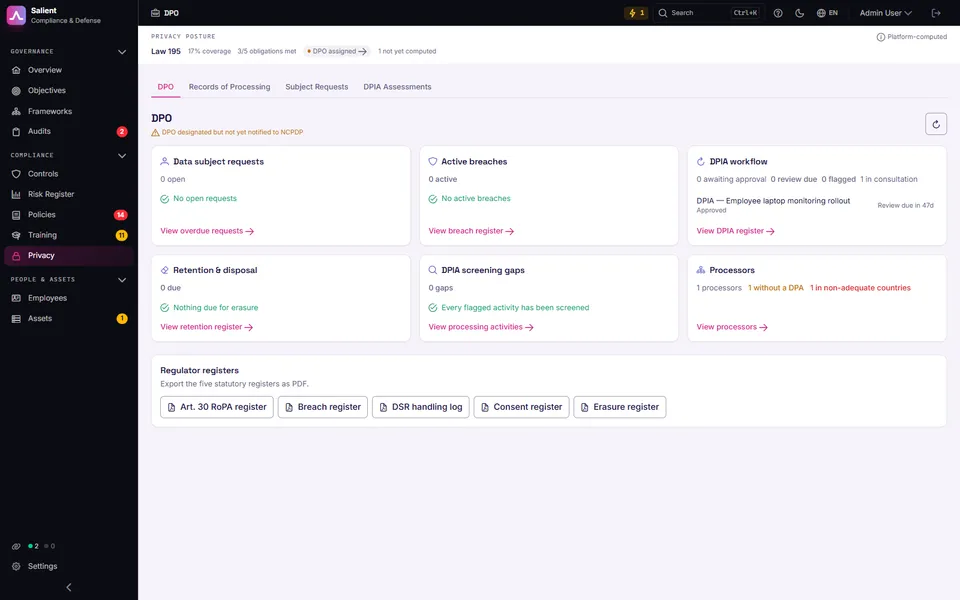
Records of processing, subject requests, DPIAs, the breach register and processors. The statutory registers export to PDF in the format your regulator asks for.

The Privacy screen: requests, breaches, DPIAs, retention, processors and the statutory registers

04 · Integrations

Evidence read straight from your systems.

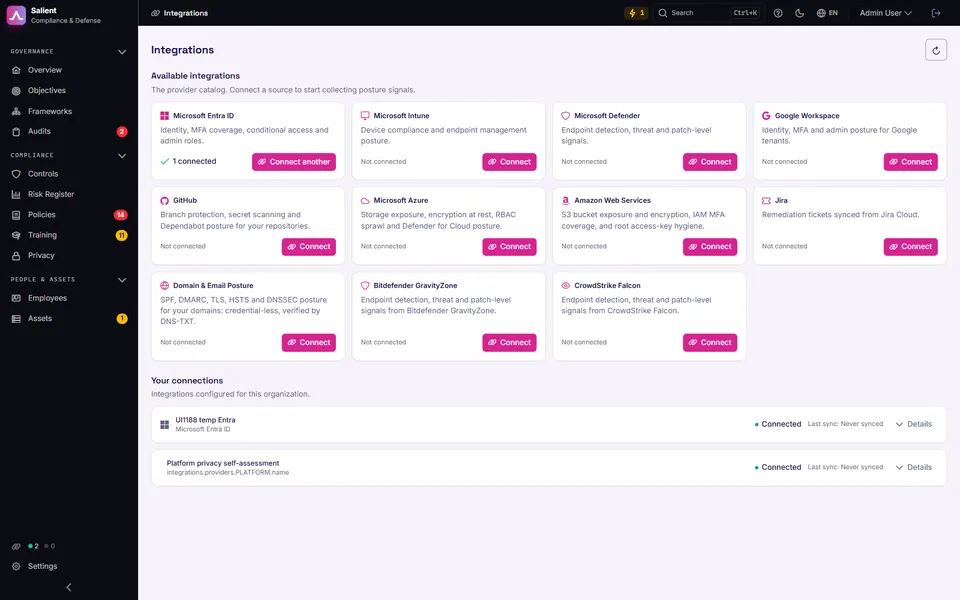
Microsoft Entra ID, Intune, Defender, Google Workspace, Azure, AWS, GitHub: the platform reads the real state of your controls - MFA, devices, access - instead of screenshots.

The Integrations screen: the connector catalogue and active connections

05 · Access

You decide who sees what.

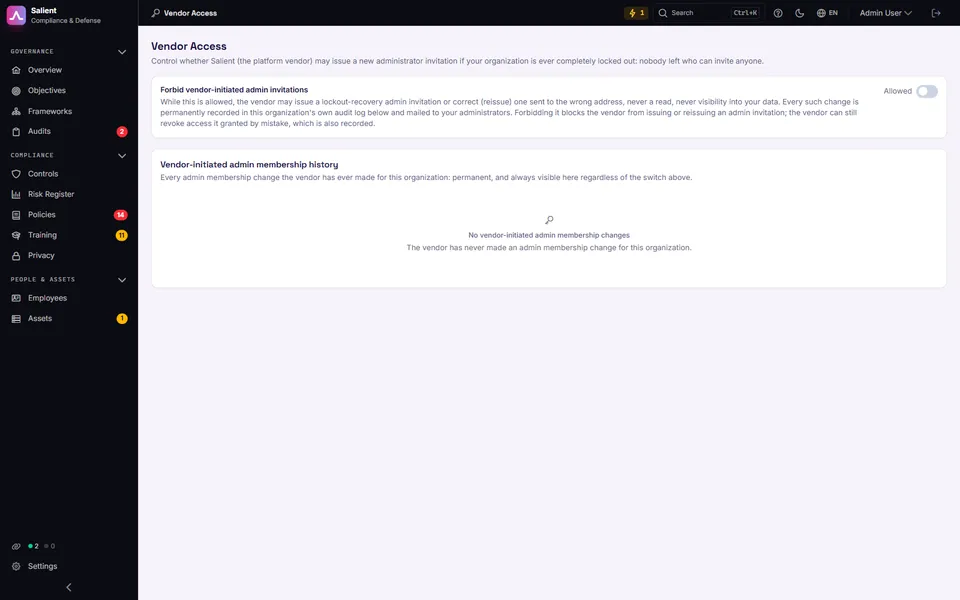
The auditor gets a read-only audit room. The platform vendor's own access can be forbidden by the organisation, and every intervention stays permanently in the audit log.

The Vendor access screen: the forbid switch and the intervention history

Frameworks covered

Built on ISO 27001, SOC 2, GDPR, NIS2, NIST CSF and CIS. Local regimes mapped on top: Moldova's Law 195/2024, Law 48/2023 with HG 562/2025, NBM Regulation 29/2025.

ISO 27001SOC 2GDPR

Join the beta

Tell us which laws apply to you and how many people you are. We set up your organization and walk you through the first framework.

Request beta access

Salient.sec is in open beta: we already run it with our first clients and build it at their pace.